ON THIS PAGE (7 SECTIONS)
- ✓Unifying task tracking, contextual discussion, and time logs into a single data model eliminates cross-tool context drift.
- ✓Device fingerprinting and session binding provide resilient security without relying solely on ephemeral cookies.
- ✓An immutable action audit log ensures strict operational accountability across enterprise workflows.
- ✓Vasiva follows a sequential shipping discipline: completing foundational products before launching subsequent software.
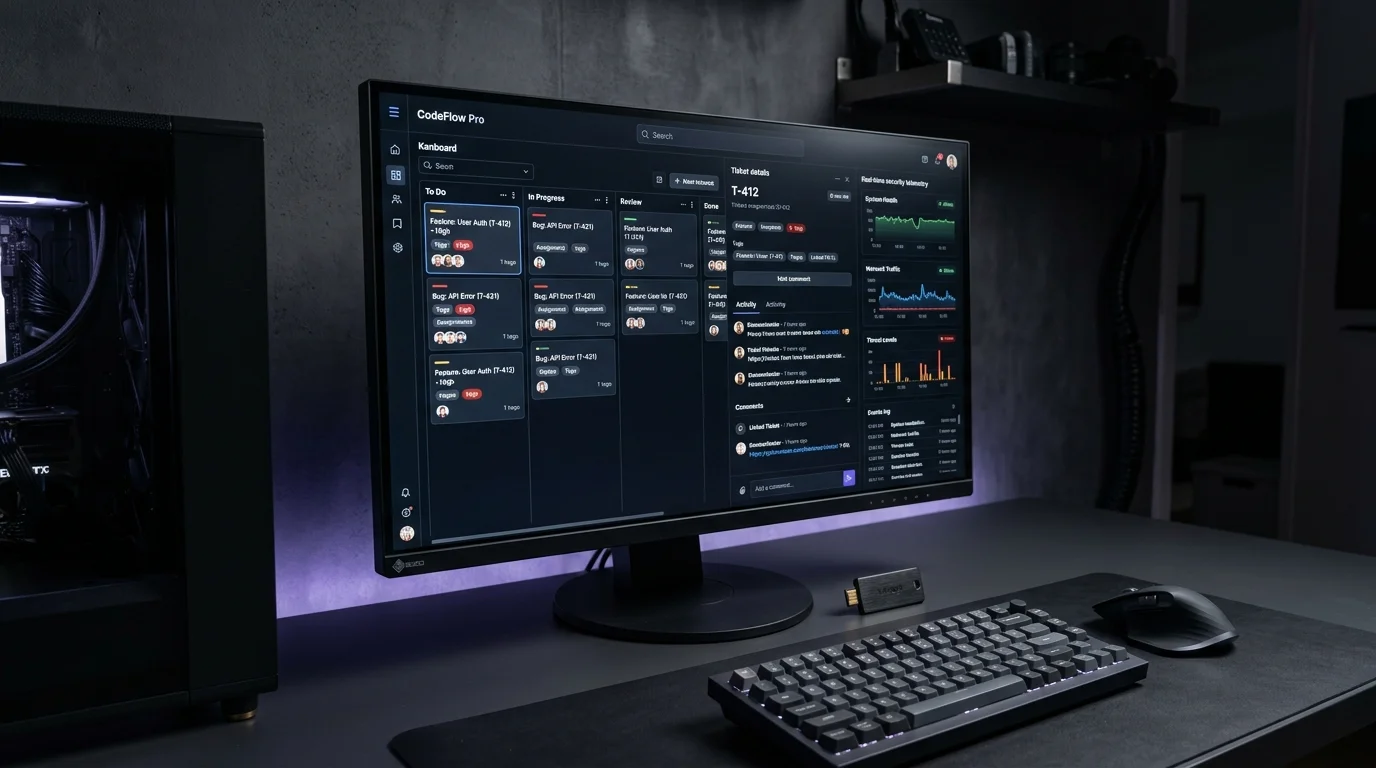
WorkHub is Vasiva's first shipped software product, running in production at work-hub.xyz. It was designed to solve an operational reality that software teams encounter daily: context fragmentation. When tickets live in one tool, conversations happen in Slack, and time tracking sits in a third application, teams spend more time synchronizing status than executing work.
Rather than attempting to reinvent database internals or claim proprietary machine learning breakthroughs, the engineering achievement of WorkHub lies in its system boundary: delivering a unified operational surface where strict session security and audit accountability are foundational constraints rather than secondary plugins.
Operational Surface and System Architecture
WorkHub unifies five foundational operational capabilities into a high-performance web application:
| Subsystem | Technical Architecture | Engineering Constraint |
| Work Item Engine | Relational ticket and project hierarchy in PostgreSQL | Strict parent-child state transitions and deterministic permissions |
| Contextual Collaboration | Real-time thread discussions anchored directly to tickets | Zero loss of conversational context; messages belong to work items |
| Session Security | Device fingerprinting and client bound tokens | Zero trust on login sessions; anomaly detection on device mismatch |
| Audit Logging | Append-only immutable event journal | Every create, edit, state transition, and delete permanently recorded |
| Production Delivery | Containerized deployment with continuous health monitoring | Deterministic releases without multi-tenant downtime |
Key Architectural Decisions and Tradeoffs
Every engineering system represents a series of intentional tradeoffs. Here are the core decisions that define WorkHub:
| Decision Domain | Chosen Architecture | Rejected Alternative | Technical Rationale |
| System Scope | Integrated tickets, chat, and time tracking in one model | Separate best-of-breed tools connected via webhooks | Integration glue creates latency, sync failures, and context loss. |
| Release Discipline | Sequential focus: Ship WorkHub completely first | Simultaneous parallel MVP development | Maintainability, security review depth, and code quality. |
| Authentication | Device-level session verification | Standard password-only cookie sessions | Strict enterprise security constraint: eliminate session hijacking. |
| Auditability | Complete immutable action audit log | Sparse activity feeds with ephemeral TTLs | Enterprise compliance requires verifiable action history. |
| Proof Standard | First-party verifiable Product Case Record | Fabricated external client logos | Engineering integrity is non-negotiable at Vasiva. |
Session Security: Device Fingerprinting in Practice
Traditional web applications rely entirely on bearer session cookies. If a session token is leaked via a malicious browser extension or network interception, attackers can impersonate legitimate users without detection. WorkHub implements device-level session verification:
- During authentication, the client computes a cryptographic hardware profile combining browser attributes, screen metrics, and WebGL canvas signatures.
- The session token in Redis is bound to this device profile fingerprint and IP subnet range.
- If an incoming request presents a valid session token but originates from an altered device fingerprint, the session is invalidated and requires step-up verification.
- All verification attempts are logged in the immutable audit stream for security telemetry.
Verification and Measurable Reality
In accordance with our engineering honesty policy, we separate verified facts from unmeasured metrics:
| Verification Point | Status | Source of Truth |
| Live Production Deployment | VERIFIED | Production application active at work-hub.xyz |
| Device Fingerprinting Session Security | VERIFIED | Implemented in WorkHub auth microservice |
| Immutable Action Audit Logging | VERIFIED | PostgreSQL append-only audit tables |
| Sequential Shipping Discipline | VERIFIED | Shipped prior to AimHabits, TalkBetter, and Dima |
| Active Monthly Enterprise Users (MAU) | [EVIDENCE REQUIRED] | Data retained internally; not published without telemetry audit |
| External Enterprise Case Studies | Not Applicable | First-party product; we do not fabricate client logos |
Core Lessons from Building WorkHub
- Ship completely before beginning subsequent products: Divided engineering attention creates fragile software. WorkHub established the architectural standards for all subsequent Vasiva products.
- Conversations must live directly on the work item: Decoupling discussions into external chat platforms destroys context and leads to unrecorded decisions.
- Security and audit trails must be designed on day one: Retrofitting device-level session binding and append-only audit logs onto an existing application is vastly more expensive than building them as core constraints.
How WorkHub Informs Vasiva's Methodology
WorkHub is not merely an internal product; it is the operational foundation for how Vasiva builds software. When enterprise clients engage us for Product Engineering or Internal Tool Development, they benefit directly from the production-tested session security, audit trails, and data structures we perfected in WorkHub.
References & Prior Art
Web Authentication: An API for Accessing Public Key Credentials (WebAuthn Level 3)
W3C Web Authentication Working Group • World Wide Web Consortium (W3C) (2024)
FIDO2: WebAuthn & CTAP Overview and Cryptographic Security Architecture
FIDO Alliance Technical Working Group • FIDO Alliance (2023)
Barath
Product EngineerBarath builds and maintains Vasiva's product engineering systems, specializing in session security, device fingerprinting, and audit logging architectures.

